Diallo Abdoul-Moumouni Open to internships

About Me

Cybersecurity & Embedded Systems · ENSA Tétouan

Final-year engineering student specializing in Cybersecurity and Embedded Systems at the National School of Applied Sciences in Tetouan, currently completing a SOC internship at NearSecure focused on automating detection and response workflows. I combine hands-on Blue Team / SOC engineering (Wazuh, DFIR-IRIS, n8n, threat intel enrichment) with a strong foundation in embedded systems and OT/ICS security, aiming to grow into a Cybersecurity/SOC Analyst or IT-OT security engineer role.

2019 – 2022

National Scientific High School of Bobo-Dioulasso (BFA)

High School Diploma in Mathematics and Physics

2022 – 2024

National School of Applied Sciences of Tetouan (Morocco)

Integrated Preparatory Classes

2024 – 2027 Current

National School of Applied Sciences of Tetouan

Engineering Cycle in Cybersecurity and Embedded Systems

Cybersecurity / SOC Tools
Wazuh DFIR-IRIS n8n/SOAR MITRE ATT&CK Suricata ELK Stack TheHive / Shuffle VirusTotal / AbuseIPDB
Programming and Web Development

C C++ Java Python SQL Bash VHDL / Verilog HTML CSS JavaScript

Technologies

AVR TMS ESP32 FPGA ADAS TCP/IP Linux Raspberry Pi Azure Cloud Google Cloud Oracle Cloud
Tools
VS Code Proteus CCS Matlab/Simulink Atmel Studio Vector Tools Wireshark Quartus / Modelsim
🇫🇷

French

Fluent

🇬🇧

English

Good command

🇸🇦

Arabic

Basic

Experience

Professional Experience

SOC Analyst Intern - NearSecure

NearSecure · July - August 2026

Designed and built a full SOC automation pipeline (SOAR) using n8n, integrating Wazuh (SIEM), DFIR-IRIS (case management), Google Gemini AI analysis, Telegram alerting, and automated HTML incident reports. Implemented alert deduplication, multi-tenant routing, and Threat Intelligence enrichment (VirusTotal/AbuseIPDB), and validated detections through Atomic Red Team simulations mapped to MITRE ATT&CK.

n8n Wazuh Threat Intel

Extracurricular Activities and Volunteering

Organizing Committee Member - 2023 Business Forum

ENSA Tétouan · Oct. 2023

Active participation in the organization of the 2023 ENSA Tétouan Business Forum as a member of the Sponsorship Committee. I contributed to identifying potential partners and sponsors, supporting logistical preparations, and coordinating with invited companies.

Communication Organization Sponsorship

Moroccan Academica Cybersecurity Competition

January 2026

Participation in the Moroccan Academica Cybersecurity Competition, ranked 126th out of 1,076 teams.

CTF Cybersecurity Competition

Alumni Platform for the National Scientific High School of Bobo-Dioulasso

Project Manager - Steering and Coordination Unit; Infrastructure and Deployment Lead

Designed and deployed an alumni network platform for the National Scientific High School of Bobo-Dioulasso, enabling users to discover alumni journeys by specialty, field, or country, create profiles, and request exchanges with volunteer alumni. As Project Manager in the steering and coordination unit, I also led the infrastructure and deployments. Visit the platform.

Volunteering Infrastructure Deployment

Projects

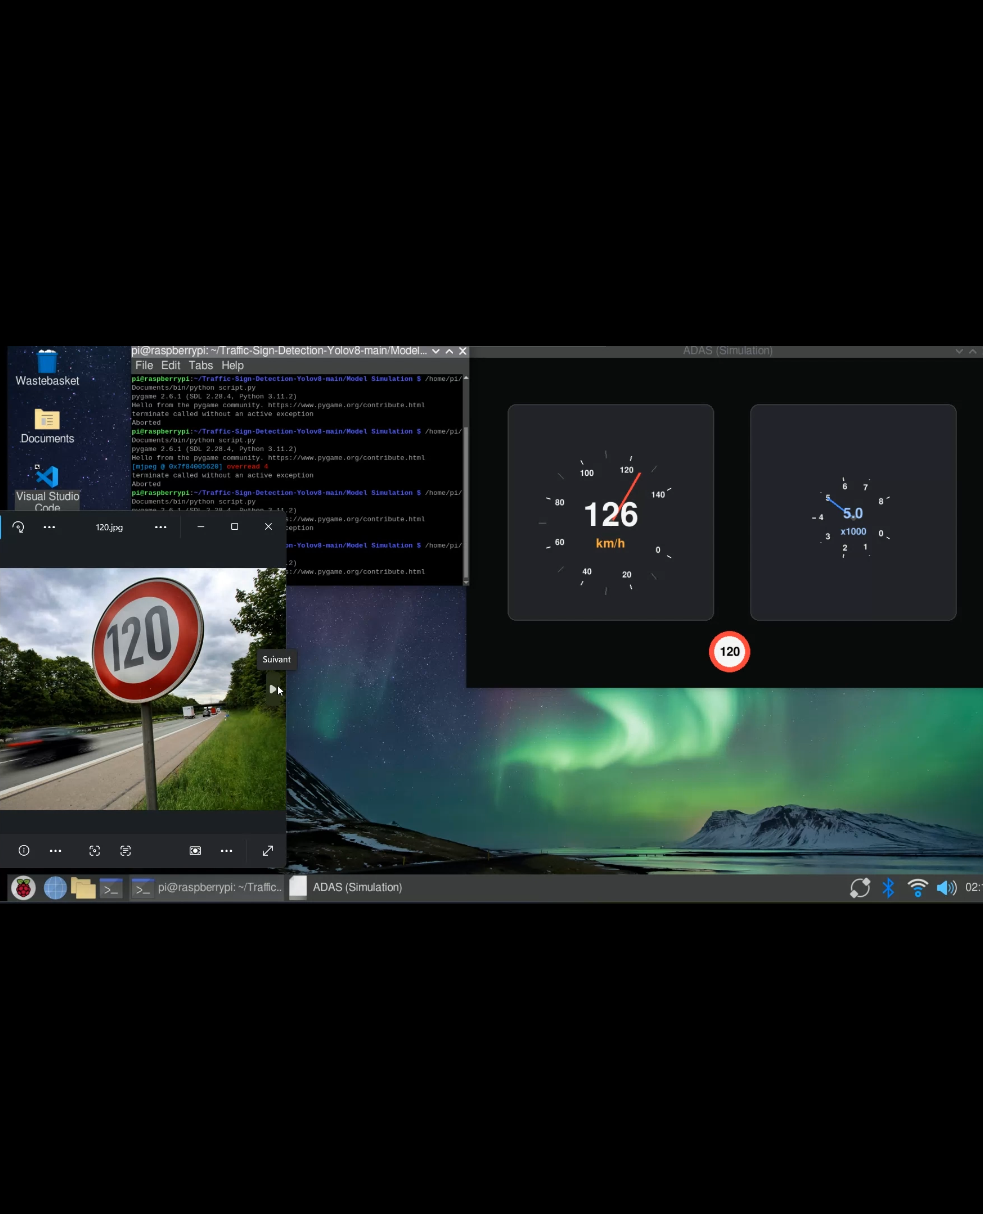
Traffic Sign Detection

Traffic Sign Detection for ADAS

YOLOv8 Python ADAS

Development of a traffic sign detection system using a YOLOv8 model, integrated into a Python interface.

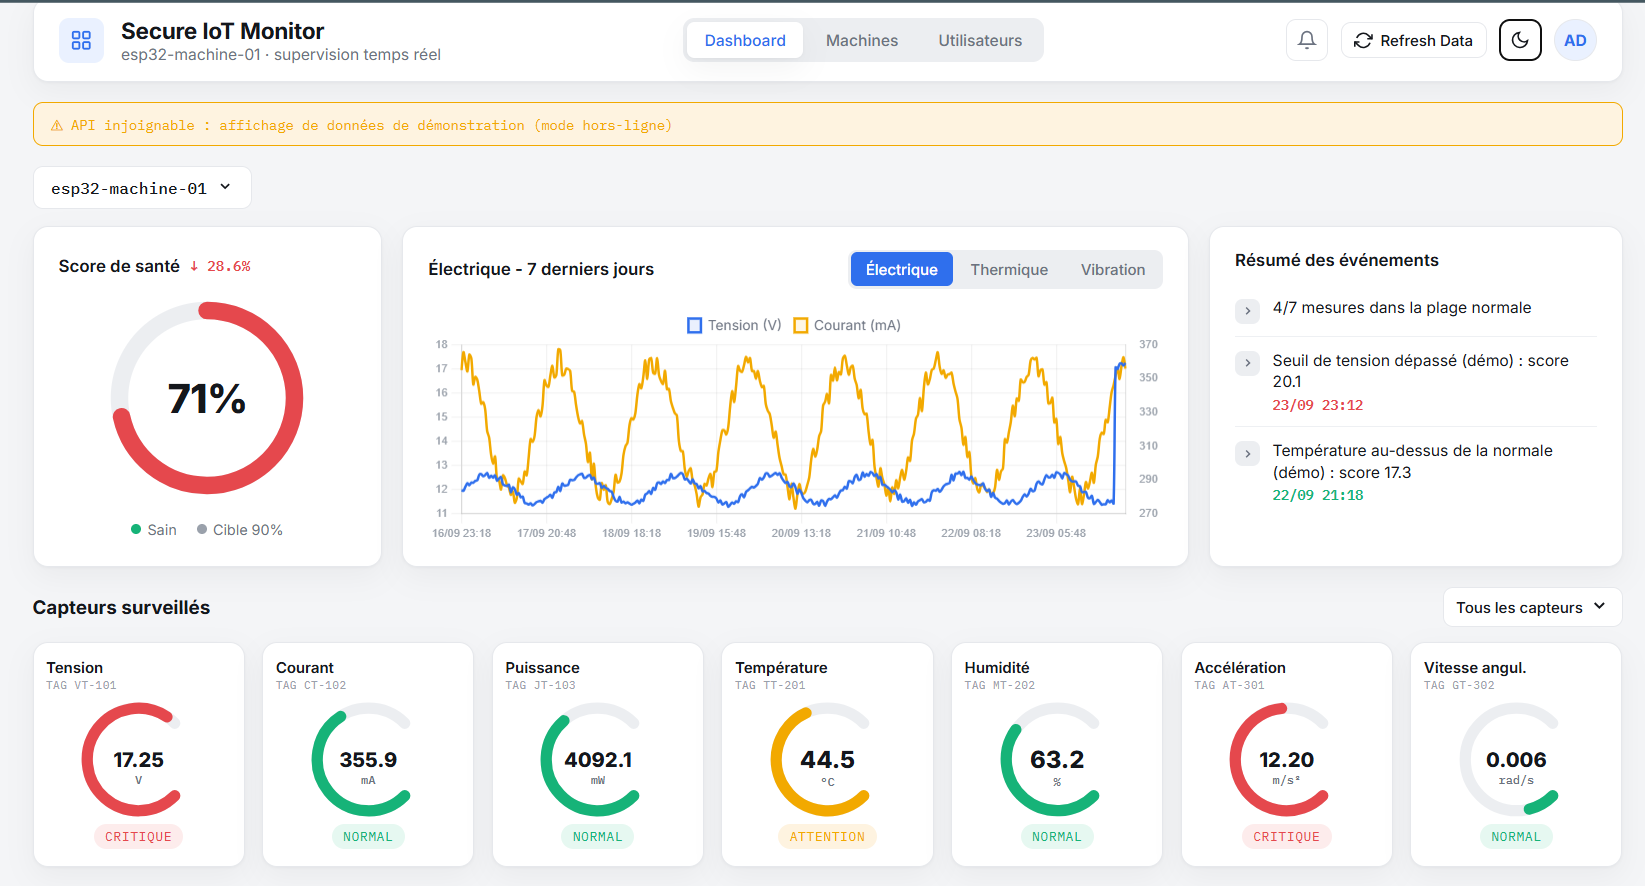
Industrial Monitoring

Embedded System for Industrial Monitoring

ESP32 Arduino IoT MQTT/TLS

Secure embedded system for industrial machine monitoring: ESP32 sensors (vibration, temperature, power) publishing over MQTT/TLS to a Raspberry Pi running LSTM-based anomaly detection, with email alerts and a real-time monitoring dashboard.

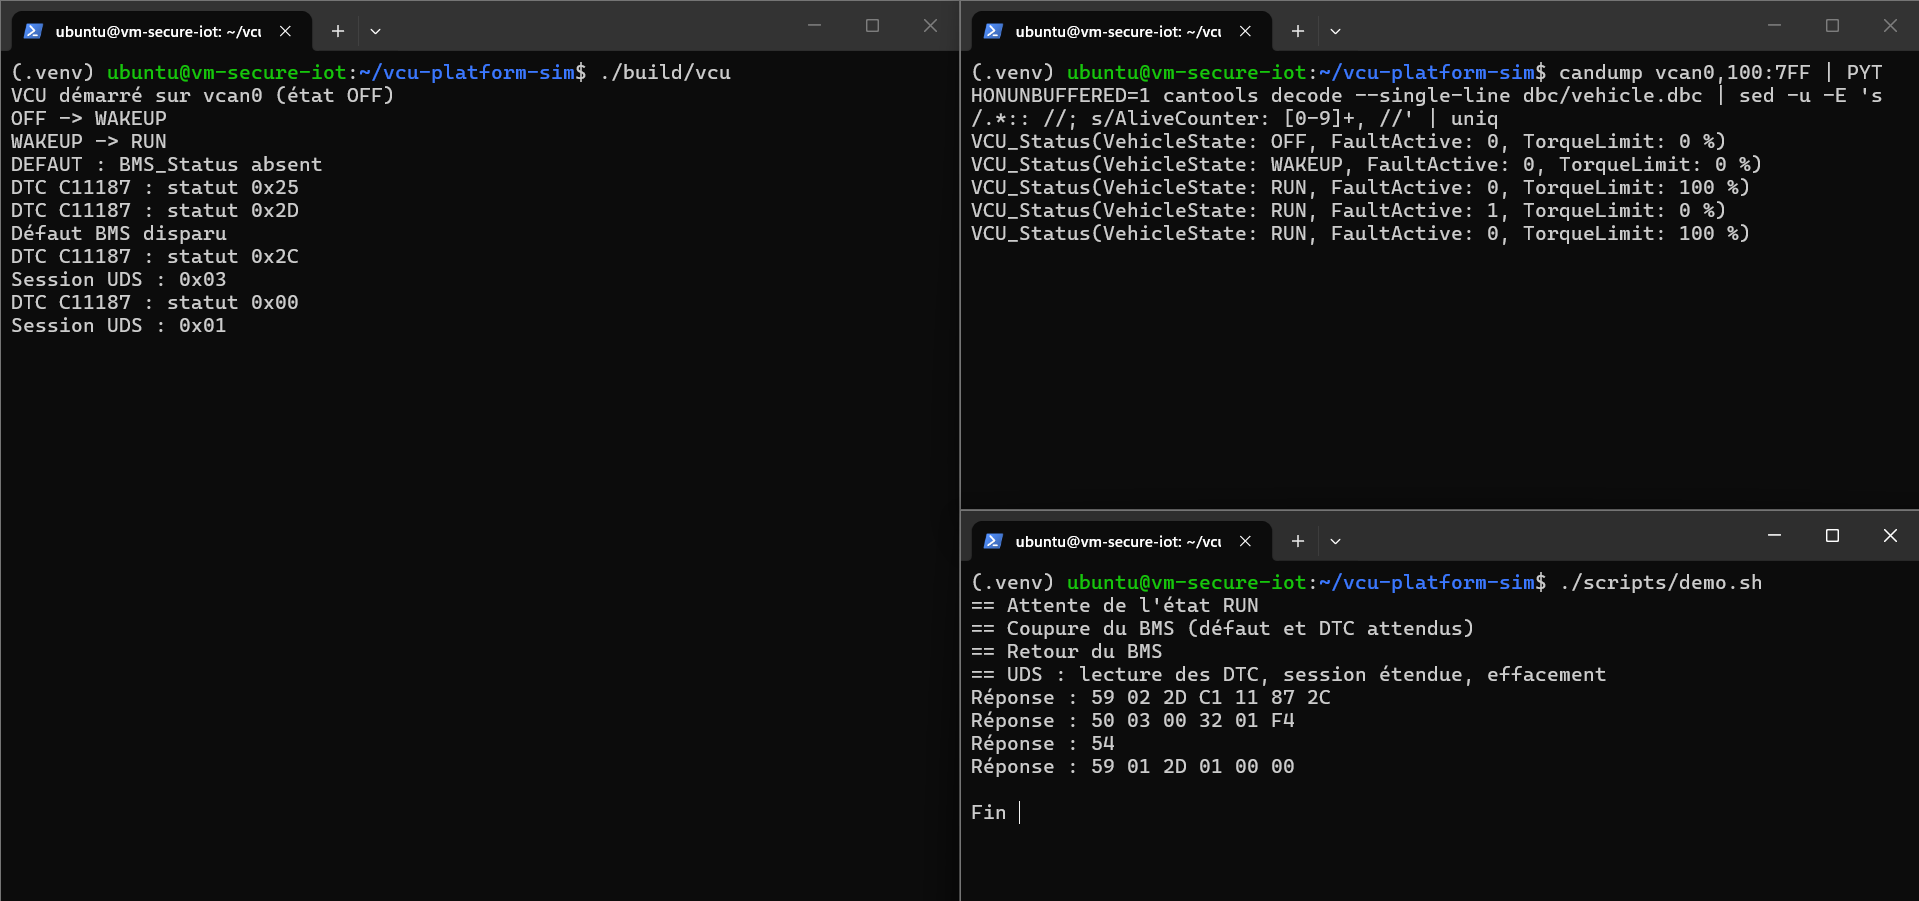
VCU Platform Simulator

VCU Platform Simulator

C++ SocketCAN UDS Linux

Simulated vehicle control unit (VCU) software platform running on Linux over a virtual CAN bus (SocketCAN, vcan0), with a DBC interface, layered C++ architecture, vehicle state management, fault management with DTCs, a minimal UDS diagnostic server, and automated tests.

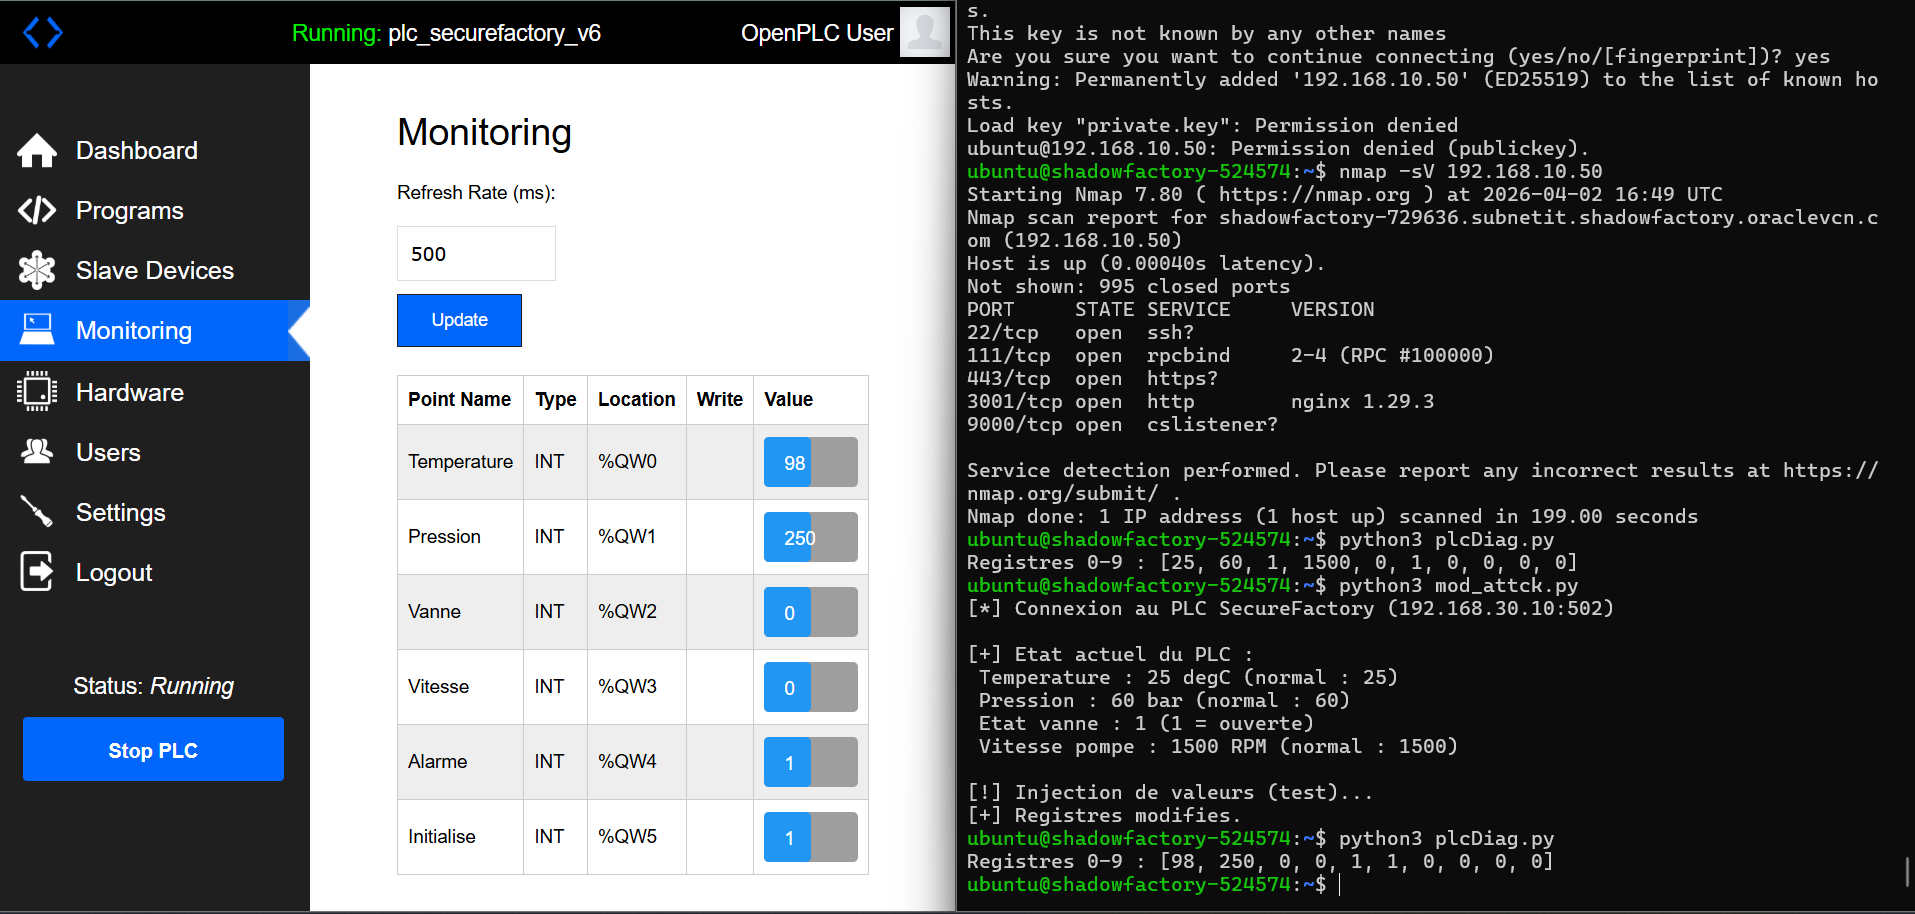
Red Team / Blue Team OT/ICS

Red Team / Blue Team on Industrial Infrastructure (OT/ICS)

Wazuh Modbus TCP TheHive

Full attack simulation on a virtual industrial infrastructure (6 VMs, Oracle Cloud), inspired by Stuxnet. Red Team executed a complete kill chain against a simulated Modbus TCP PLC; Blue Team deployed and operated a full open-source SOC stack (Wazuh, ELK, TheHive, Shuffle) for real-time detection and response.

Red-Blue-Automation OT/ICS

Red-Blue-Automation for OT/ICS

Zeek Wazuh Tracecat Local LLM

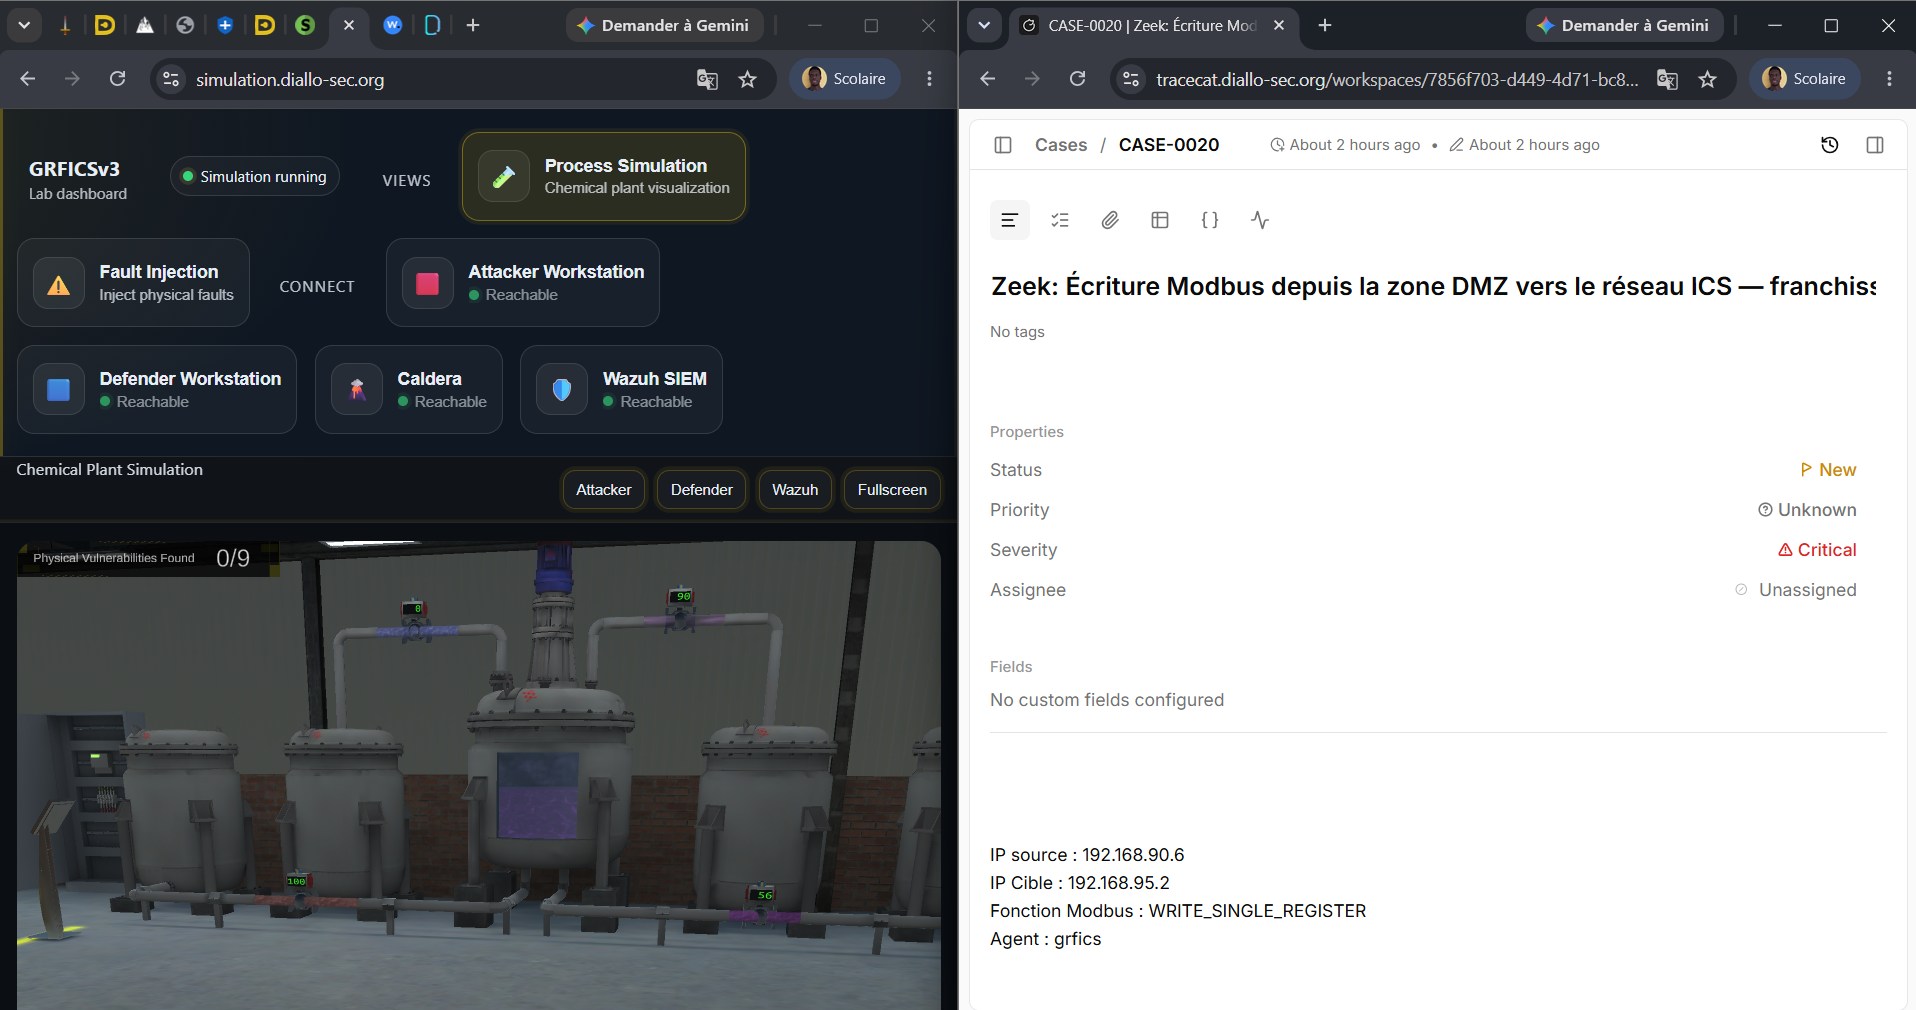
Reconstruction of an OT/ICS security lab on OCI: Blue Team detection with Zeek and Wazuh on GRFICSv3 simulated chemical processplant, plus an explicitly invoked Red Team agent using a local CPU-only LLM to select and verify fixed attack techniques through the Wazuh REST API. A Tracecat workflow orchestrates the entire process with human-in-the-loop decision validation.

SOC Automation SOAR

SOC Process Automation (SOAR) with n8n

n8n DFIR-IRIS Gemini AI

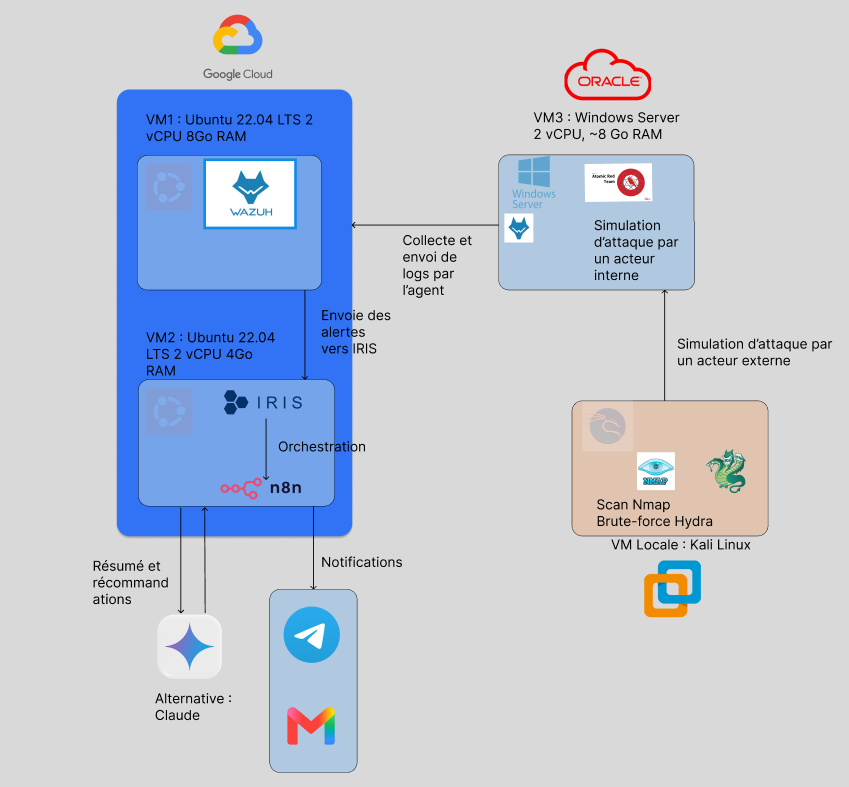
End-to-end SOC automation pipeline connecting Wazuh, DFIR-IRIS, n8n, and Gemini AI for alert triage, AI-assisted analysis, Telegram/email notification, and Threat Intelligence enrichment, tested against real attack simulations (Atomic Red Team).

IDS/IPS Suricata

IDS/IPS Deployment with Suricata on Azure

Azure Suricata IDS/IPS

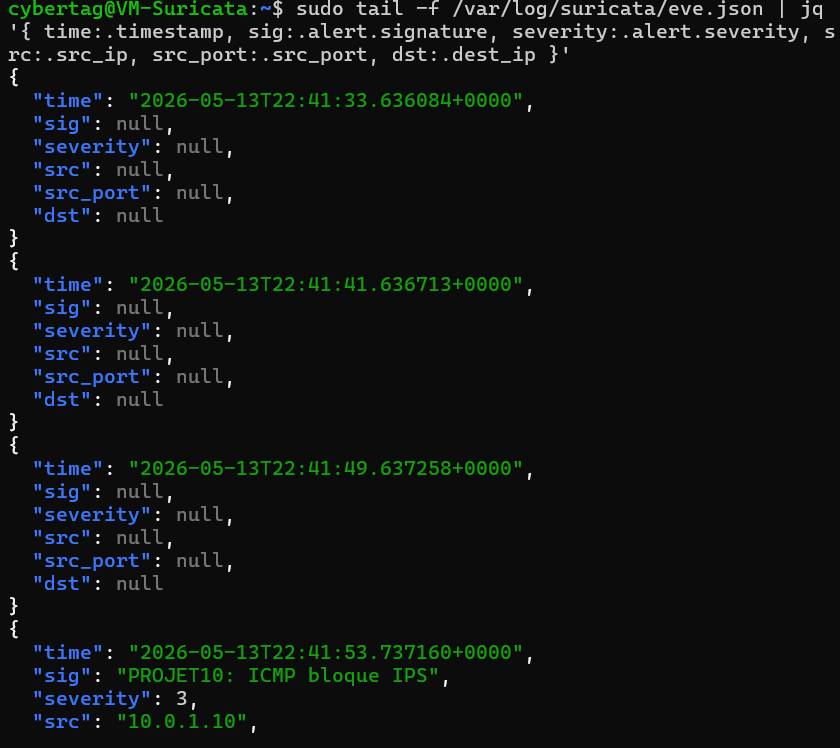
Deployment and hardening of Suricata in IPS mode via NFQueue on Azure, with log analysis (jq) and validated SSH brute-force blocking using Hydra.

IoT Anomaly Detection

Satelite telemetry Anomaly Detection System

IoT Machine Learning

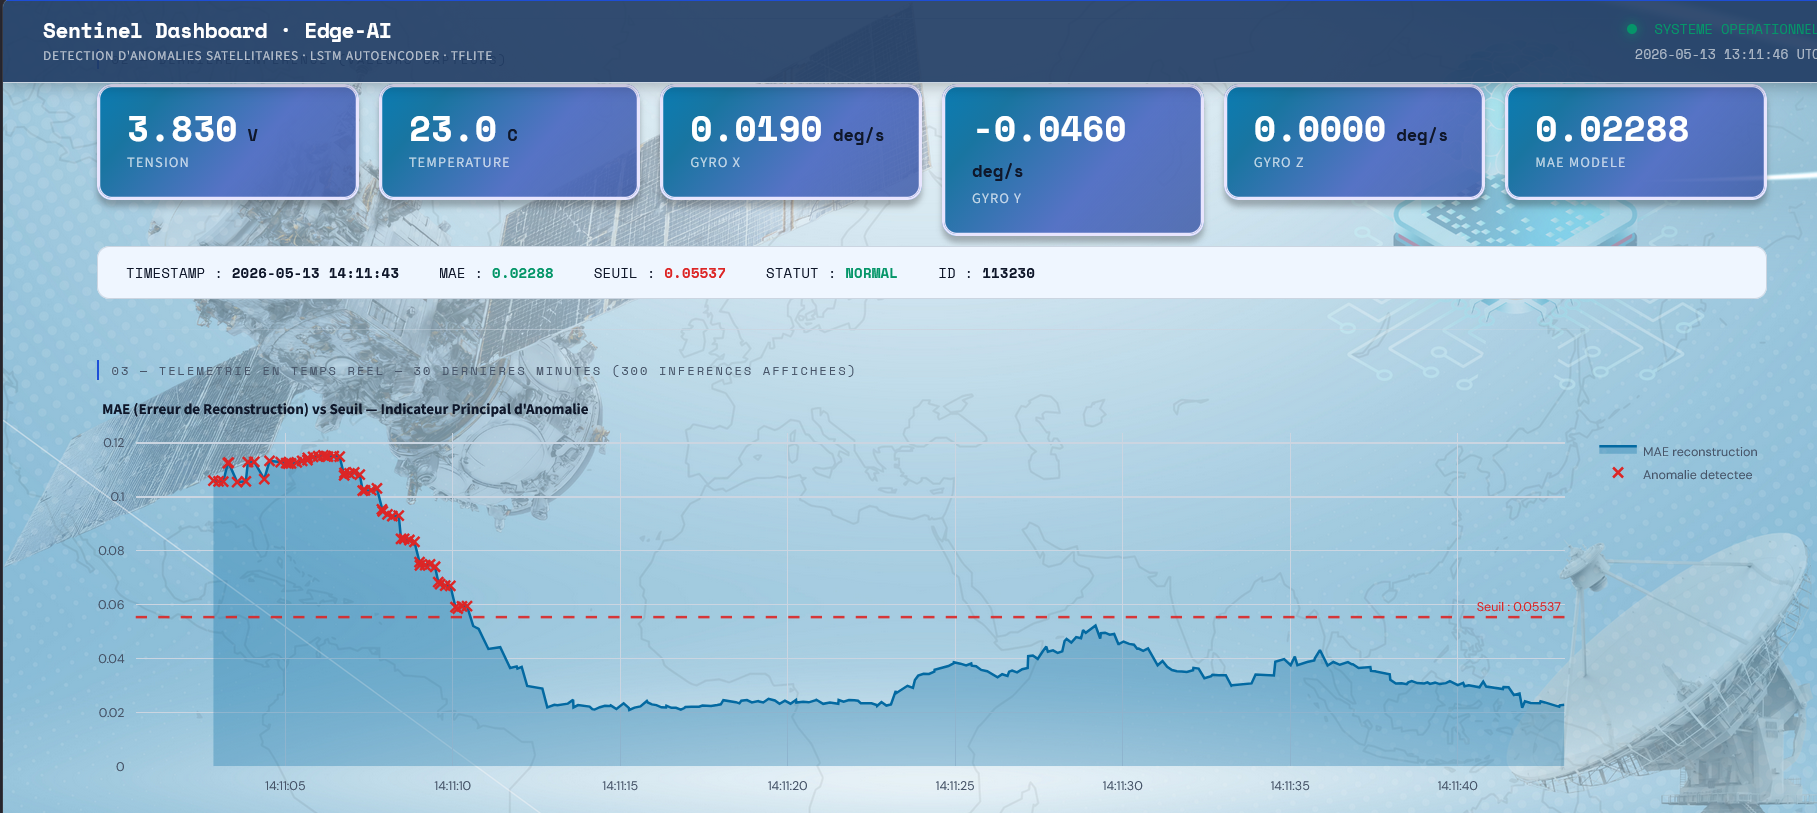
Group project building an anomaly detection system for satellite telemetry measurements on an edge platform: ESP32 firmware and a quantized LSTM autoencoder (TFLite) served through FastAPI on a Raspberry Pi 5.

VaultGCSE2

VaultGCSE2 - Hybrid AES/RSA Encryption System

AES RSA Cryptography

Custom-built hybrid encryption system combining AES and RSA for secure data storage and exchange.

See more

Certifications

Microsoft

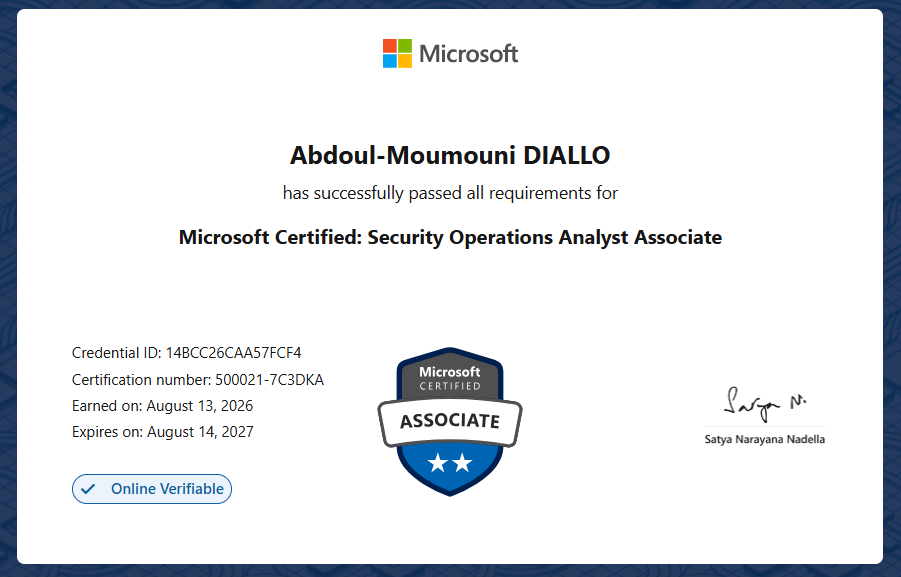
Microsoft Certified: Security Operations Analyst (SC-200)

Threat detection, investigation, and response using Microsoft Sentinel, Microsoft Defender XDR, and Defender for Cloud, with KQL-based threat hunting and incident remediation.

Microsoft

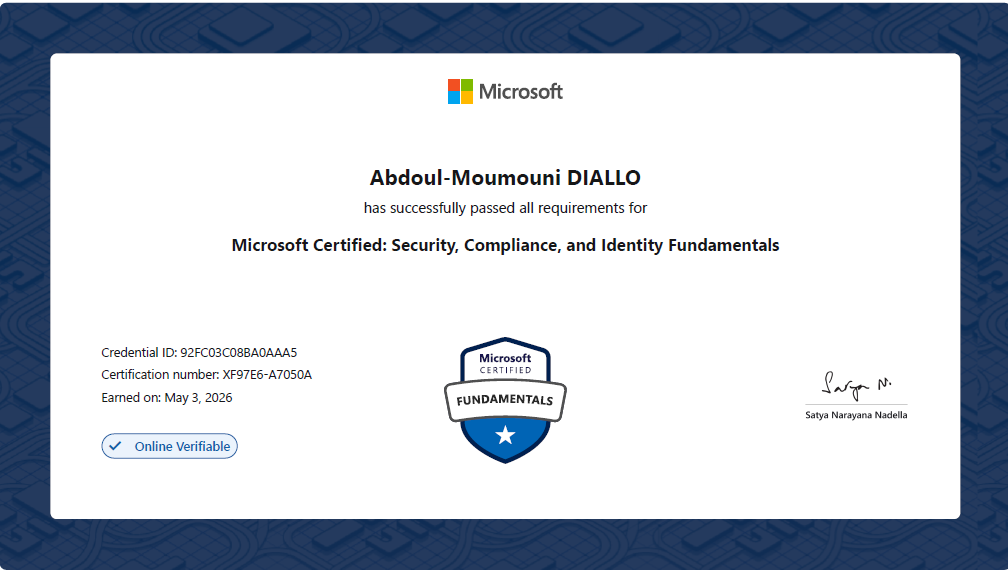
Microsoft Certified: Security, Compliance, and Identity Fundamentals (SC-900)

Foundational knowledge of security, compliance, and identity concepts across Microsoft cloud services.

Microsoft

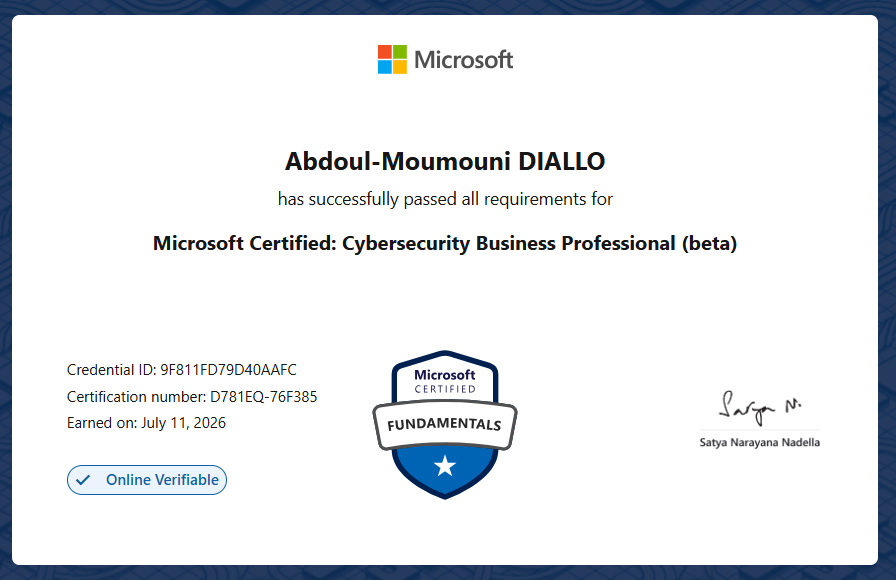
Microsoft Certified: Cybersecurity Business Professional (beta)

Foundational cybersecurity awareness for business roles: identifying threats and risks, handling sensitive data safely, applying access controls, and reporting and responding to security incidents.

IBM

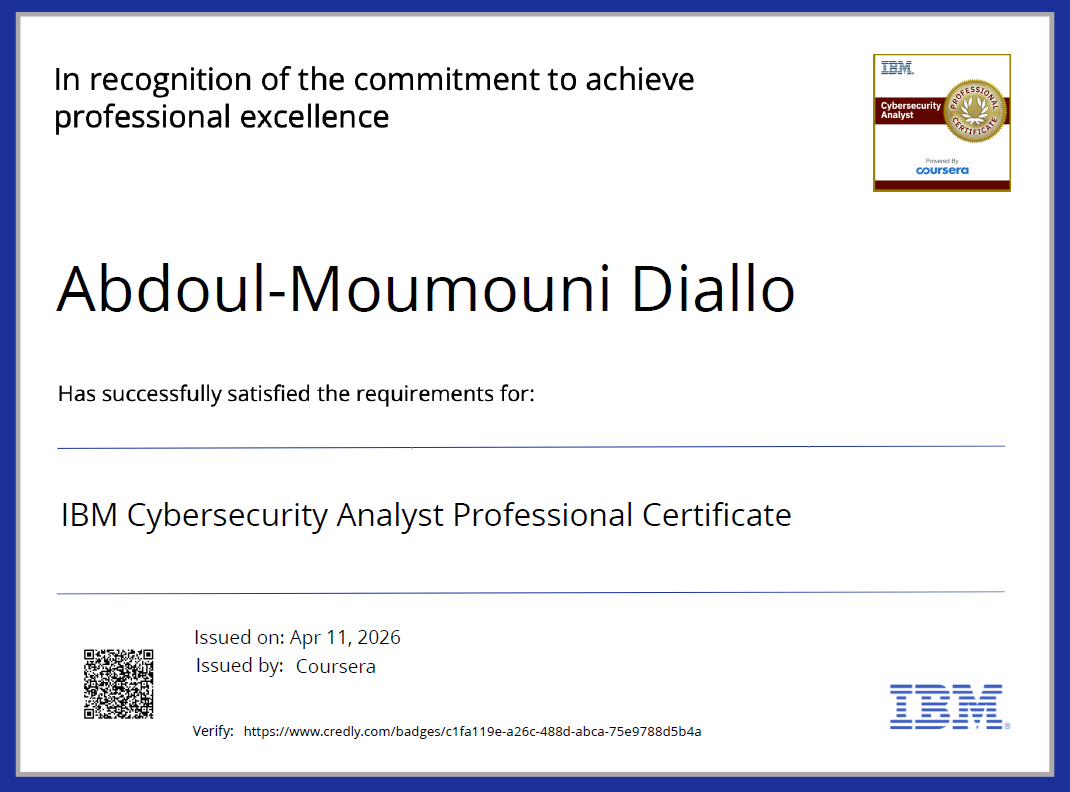
IBM Cybersecurity Analyst Professional Certificate

SOC operations, incident response, SIEM tools, network security, penetration testing fundamentals, and threat intelligence.

Microsoft

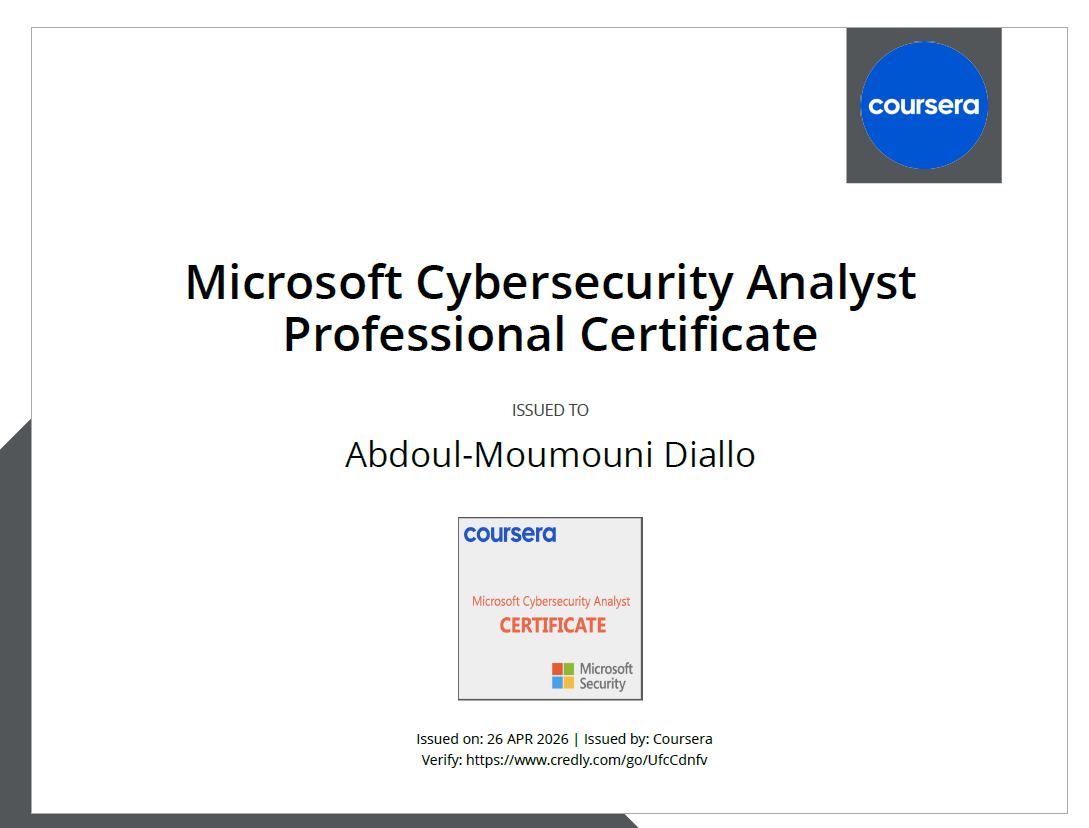
Microsoft Cybersecurity Analyst Professional Certificate

Threat detection, security operations, identity and access management, and Microsoft security tooling.

(ISC)²

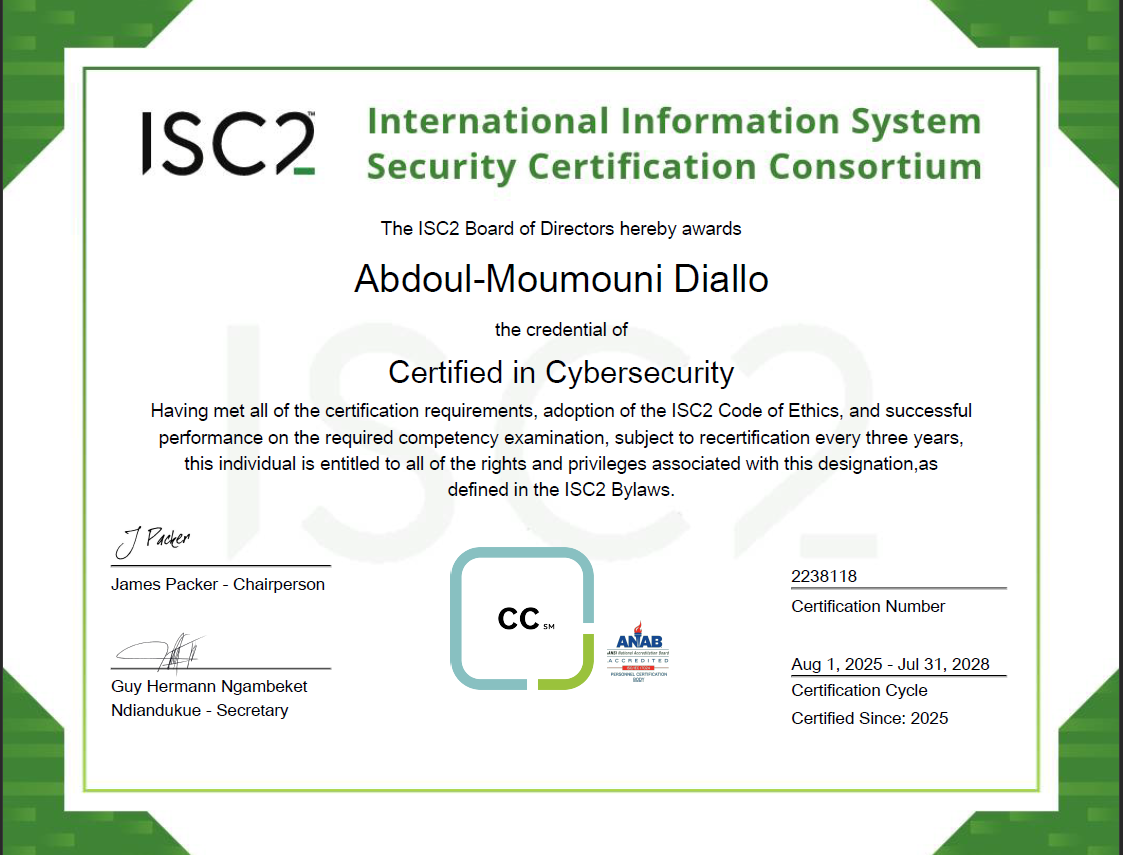
Certified in Cybersecurity (CC)

Security Principles, Business Continuity and Disaster Recovery, Access Control Concepts, Network Security, Security Operations

Udemy

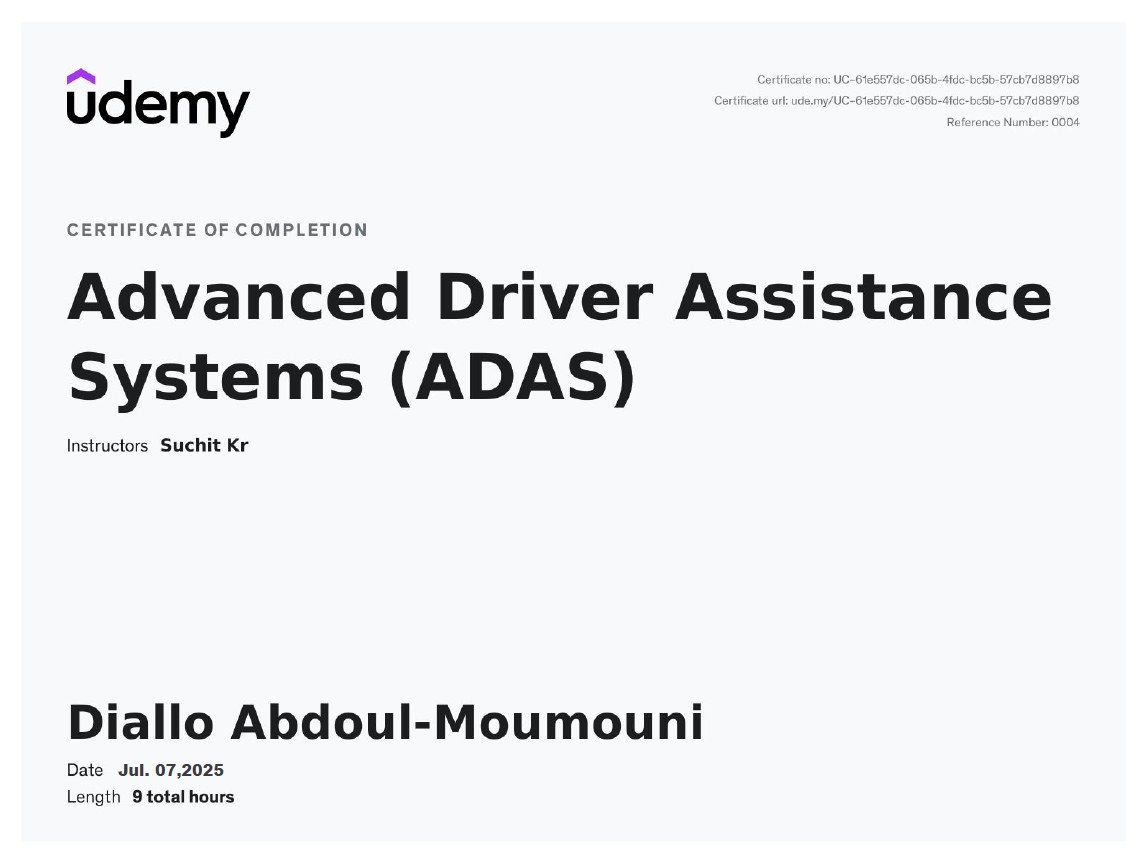
Advanced Driver Assistance Systems

Sensors, systems study, testing and validation

Cisco

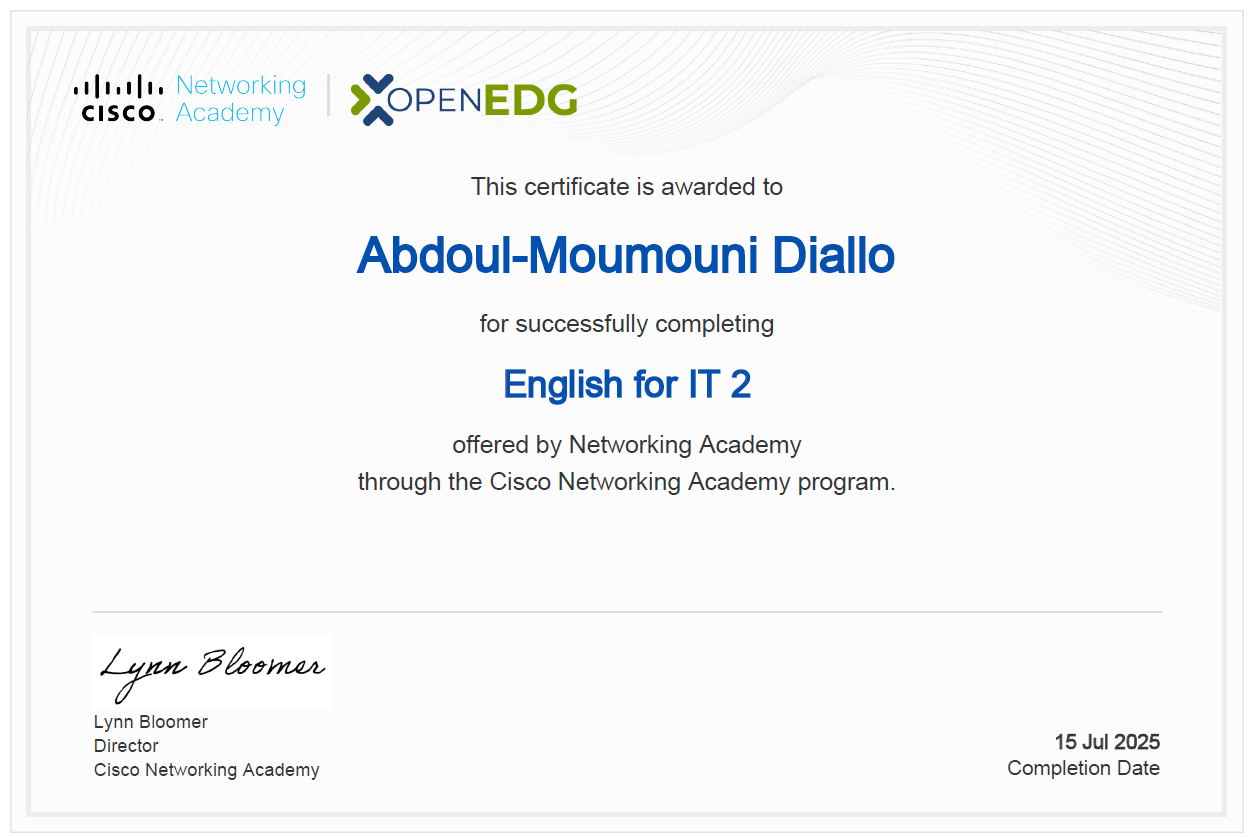
English for IT 2

Technical vocabulary, IT communication skills, Listening and speaking in tech context, Collaboration in global teams

View all certifications

Contact me

dialloabdoulmoumouni@gmail.com
+212 642983576
Download CV